
SSHepherd Documentation
Protecting Apache Web Server
Applies to SSHepherd 2.0
Overview
Apache Web Server runs a large share of the world’s web sites, so attackers scan for it constantly. With SSHepherd®, Apache listens only on the host itself, and authorized users reach it through a Generic tunnel. The web server keeps working for them, with no open port for anyone else to find.
Before you start
- The SSHepherd® Agent is installed on the Apache server.
- The Control App or shepctl is installed on the user’s computer.
- The user and the Apache server are in the same SSHepherd® group, or the user has a Generic tunnel definition for it.
- You’ve checked that the user can open an SSHepherd® tunnel to the server.
Configure the Apache server
These steps are for Apache on Debian or Ubuntu.
- Make Apache listen only on localhost. Edit
ports.conf:sudo nano /etc/apache2/ports.confChange theListenline to:Listen 127.0.0.1:80 - Save the file and restart Apache:
sudo systemctl restart apache2 - Allow port 80 on the agent:
- In the Administrator Console, click Agents and select the Apache server.
- Click the Settings tab.
- Add
80to Allowed Ports. - Click Save.
That’s all the setup the Apache server needs.
Access the web server with shepctl
- Sign in with shepctl and open a tunnel, here on local port 8080:
shepctl --hostname <apache server host name> --relayport 80 --port 8080 tunnel - In a web browser, open
http://127.0.0.1:8080. The site’s home page loads. - Press Ctrl+C to close the tunnel. The site is no longer reachable until you open another tunnel.
Access the web server with the Control App
- Ask your administrator for a Generic tunnel definition with To Agent set to the Apache server, Remote Host
127.0.0.1and Remote Port80. See Tunnel Definitions. - In the Control App, switch the tunnel on.
- Open
http://127.0.0.1:<local port>in a browser, using the tunnel’s local port.
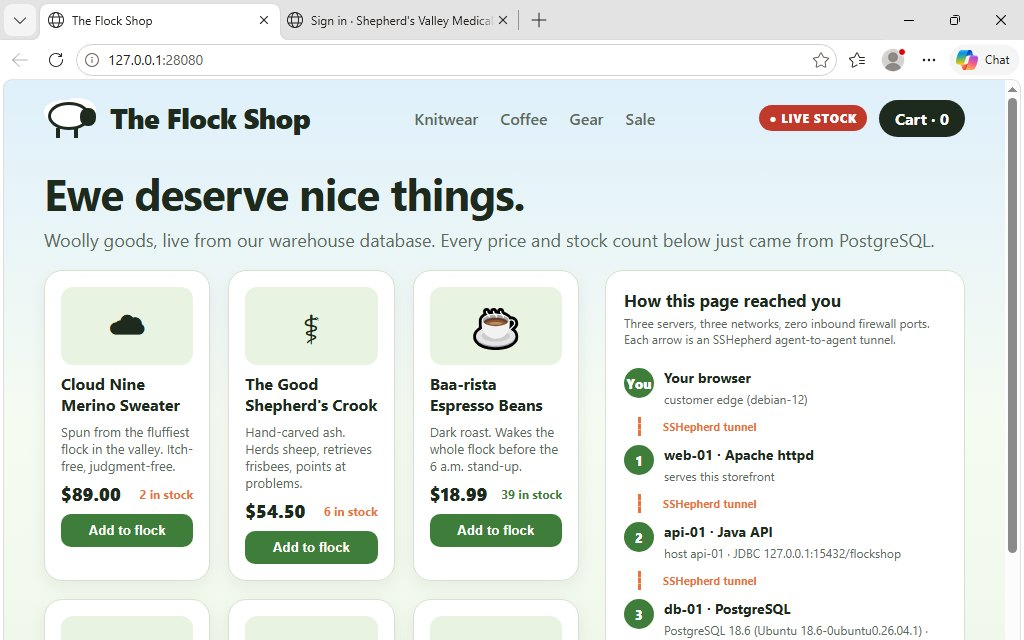
Because of the way SSHepherd® works, you can do the same with almost any application that can listen on a specific port.